Automotive Development Agents

汽车工程智能体工具包 Automotive engineering agent toolkit

面向自动驾驶安全、SOTIF、中国标准、场景驱动测试和工程证据链,把汽车研发中的专家角色、技能、规则、命令、工作流和知识库沉淀为可复用的开源智能体资产。 An open-source agent asset base for automated-driving safety, SOTIF, China standards, scenario-driven testing, and engineering evidence workflows, organizing expert roles, skills, rules, commands, workflows, and knowledge references for automotive development.

75+技能类别 / Skill groupsSkill groups / 技能类别 33工程命令 / CommandsCommands / 工程命令 26工作流 / WorkflowsWorkflows / 工作流 100+知识库文档 / Knowledge docsKnowledge docs / 知识库文档

前身为 Automotive Claude Code Agents;本页采用更通用的项目名,同时保留上游开源项目 credit 和许可证边界。 Formerly explored as Automotive Claude Code Agents; this page uses a broader project name while preserving upstream credit and license boundaries.

标准密集 Standards density

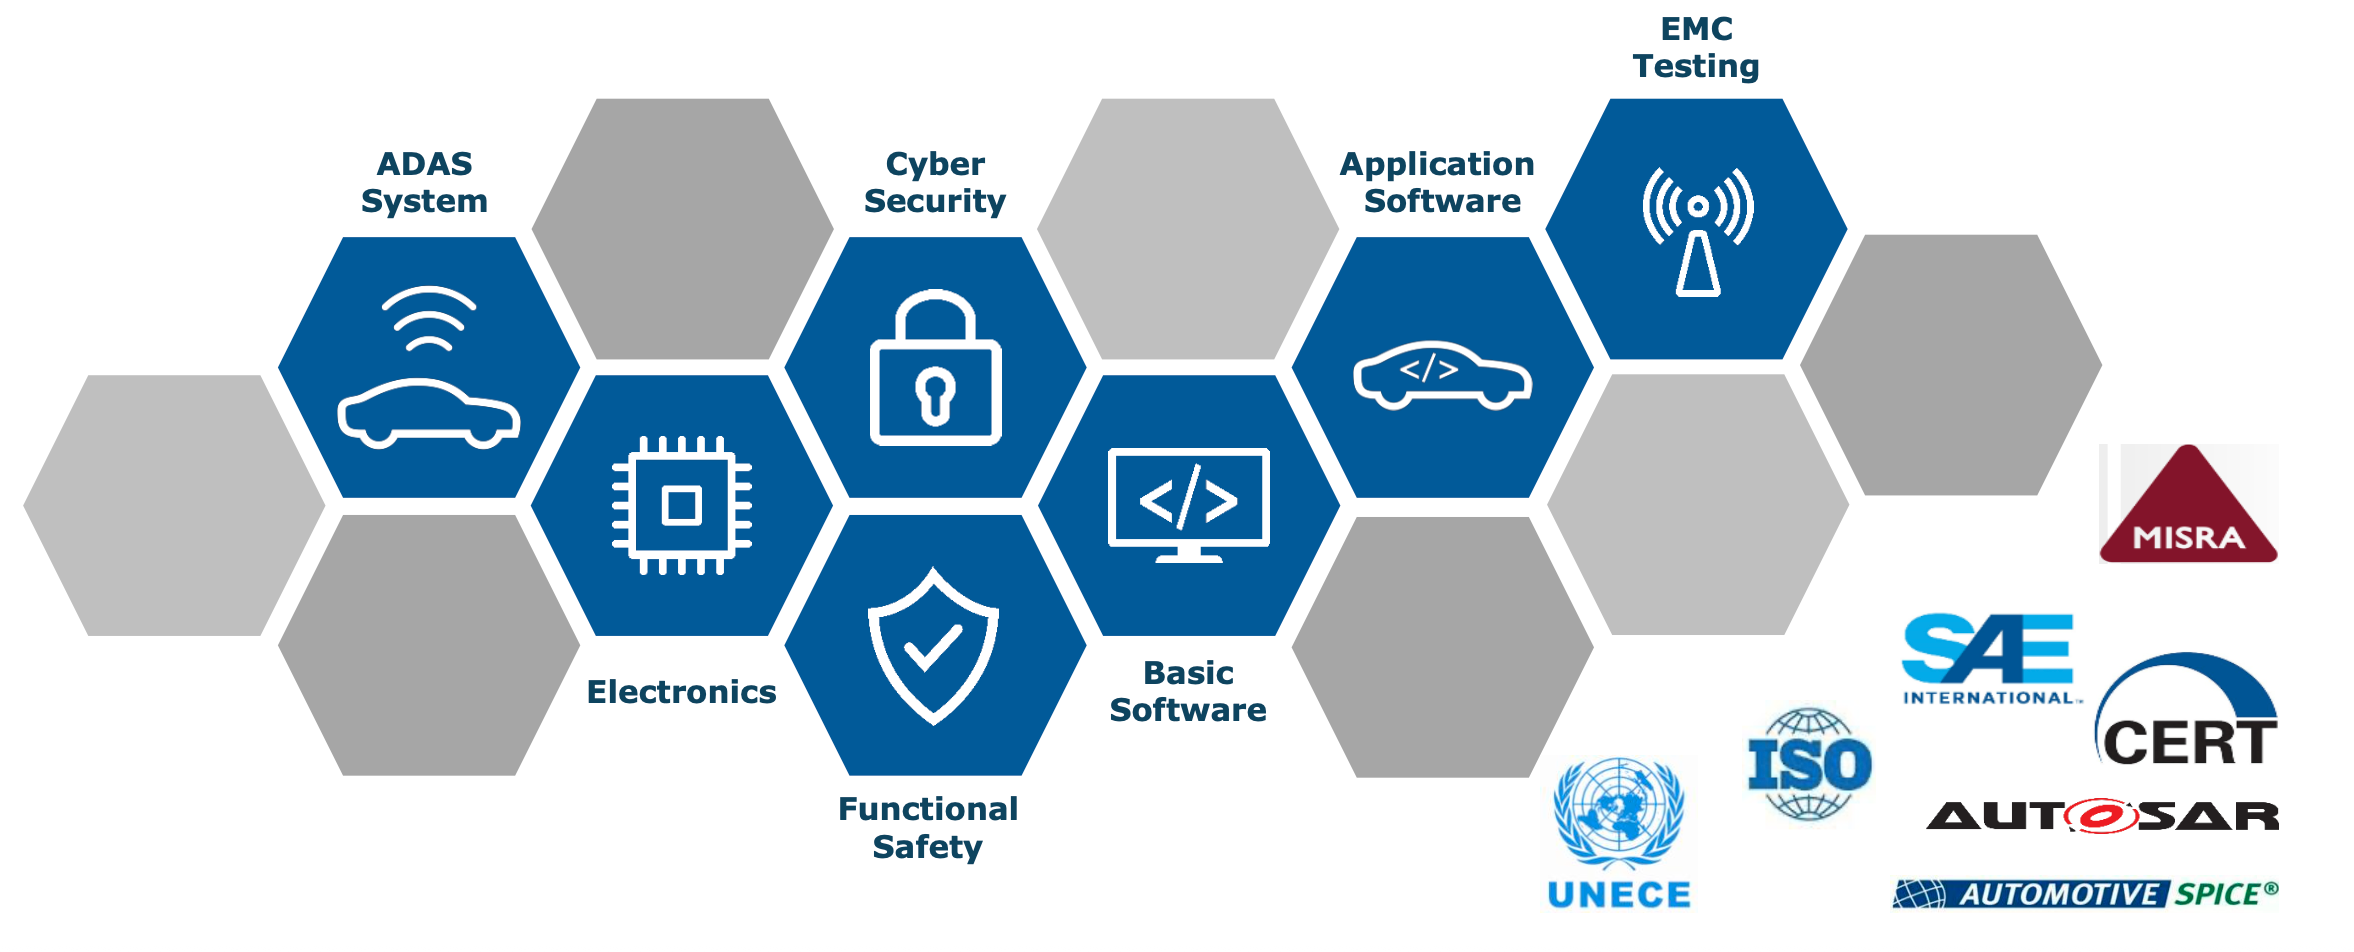
汽车不是低门槛的软件行业。ADAS、功能安全、网络安全、EMC、AUTOSAR、MISRA、ASPICE、UNECE 等标准和过程要求交织在一起,每个工程判断都需要同时考虑系统、软件、硬件、验证和证据边界。 Automotive engineering is not a low-barrier software domain. ADAS, functional safety, cybersecurity, EMC, AUTOSAR, MISRA, ASPICE, UNECE, and related process requirements overlap, so engineering decisions must consider system, software, hardware, validation, and evidence boundaries together.

Automotive standards ecosystem covering ADAS, electronics, cybersecurity, functional safety, software, EMC testing, MISRA, SAE, ISO, CERT, AUTOSAR, ASPICE and UNECE

真正的壁垒,是标准、流程和证据同时成立 The real barrier is standards, process, and evidence at the same time

这也是为什么汽车研发智能体不能只做“问答”或“代码补全”。它要把专家角色、领域技能、标准规则、过程命令和知识库组织成可复核的工程工作流。 That is why automotive development agents cannot stop at Q&A or code completion. They need to organize expert roles, domain skills, standard rules, process commands, and knowledge bases into reviewable engineering workflows.
Functional Safety SOTIF Cybersecurity AUTOSAR ASPICE UNECE

为什么需要它 Why this matters

汽车工程智能体不是通用代码补全。它需要把标准、架构、安全分析、测试评价、工程过程和证据链放进同一个可复用工作流,让工程师可以在明确边界内更快完成分析、草案和复核准备。 Automotive engineering agents are not generic code completion. They need to connect standards, architecture, safety analysis, test evaluation, engineering process, and evidence chains into reusable workflows that help engineers prepare analysis, drafts, and review materials within explicit boundaries.

Automotive engineering agent loop 标准 Standards 架构 Architecture 智能体工作流 Agent workflow 路由 · 检索 · 草案 · 复核 安全 Safety 证据 Evidence

标准密集 Standards-heavy

ISO 26262、ISO 21448、ISO 21434、AUTOSAR、MISRA、ASPICE 与中国准入要求共同约束工程判断。 ISO 26262, ISO 21448, ISO 21434, AUTOSAR, MISRA, ASPICE, and China approval requirements jointly shape engineering decisions.

流程很长 Long process chain

需求、系统架构、软件、硬件、安全、验证、配置和文档交付之间需要稳定协同。 Requirements, system architecture, software, hardware, safety, validation, configuration, and documentation need stable coordination.

知识离散 Knowledge fragments

标准理解、专家经验和项目模板如果只留在聊天中,很难变成可复用能力。 Standards knowledge, expert experience, and project templates are hard to reuse if they stay only in chat history.

复核不可省 Review remains central

智能体可以整理、检索和生成草案,但安全工程结论必须由工程师复核。 Agents can organize, retrieve, and draft, but safety-engineering conclusions still require engineering review.

资产架构 Asset architecture

仓库不是单个 prompt,而是一组可安装、可路由、可复核的工程资产:技能负责知识与方法,智能体负责角色视角,规则与知识库负责边界,命令与工作流负责可重复执行。 The repository is not a single prompt. It is an installable, routable, reviewable set of engineering assets: skills carry methods, agents carry roles, rules and knowledge bases carry boundaries, and commands and workflows make repeated execution possible.

输入 Inputs

需求 / 场景 / 代码 / 标准条款 Requirements / scenarios / code / clauses

智能体资产层 Agent asset layer

技能库 Skills领域方法 智能体 Agents专家角色 规则库 Rules边界约束 工程命令 Commands任务入口 工作流 Workflows过程编排 知识库 Knowledge Base依据沉淀

输出 Outputs

分析草案 / 校核清单 / 证据记录 Draft analysis / review checklist / evidence record

01

技能库 Skills Skills

覆盖 ADAS、AUTOSAR、功能安全、SOTIF、中国标准、诊断、V2X、SDV、HPC、端到端 AD 安全等领域。 Covers ADAS, AUTOSAR, functional safety, SOTIF, China standards, diagnostics, V2X, SDV, HPC, and end-to-end AD safety.

02

智能体 Agents Agents

沉淀安全工程师、SOTIF 分析师、场景工程师、中国合规工程师、ADAS 架构师、测试验证工程师等角色。 Captures roles such as safety engineer, SOTIF analyst, scenario engineer, China compliance engineer, ADAS architect, and validation engineer.

03

规则库 Rules Rules

把安全、编码、过程、测试、安全标准和中国标准约束放到工程复核链路中,而不是只靠模型自由发挥。 Places safety, coding, process, testing, security, and China-standard constraints into the review chain instead of relying on free-form model output.

04

知识库 Knowledge Base Knowledge Base

组织标准索引、过程说明、技术参考和示例模板,为智能体输出提供可追溯依据。 Organizes standards indexes, process notes, technical references, and examples so agent outputs have traceable support.

05

命令 Commands Commands

将常见工程任务收敛为 slash commands,减少重复检索、重复解释和临时性手工流程。 Converts common engineering tasks into slash commands to reduce repeated lookup, repeated explanation, and ad-hoc manual flows.

06

工作流 Workflows Workflows

把需求分析、架构评估、安全分析、验证计划和证据沉淀串成端到端链路。 Connects requirements analysis, architecture assessment, safety analysis, validation planning, and evidence capture into end-to-end flows.

公开资产快照 Public asset snapshot

分类后的核心资产清单 Classified core asset inventory

以下不是完整文件树,而是按工程用途整理的代表性清单,用来说明这个项目已经沉淀出多层次的智能体资产,而不只是几个提示词样例。 This is not a full file tree. It is a representative engineering view showing that the project has accumulated multiple layers of agent assets rather than a few prompt examples.
60+智能体定义Agent definitions 75+技能类别Skill categories 26工程工作流Engineering workflows 100+知识库文档Knowledge docs
Agents

智能体角色族 Agent role families

  • 安全与合规:功能安全、SOTIF、中国合规、ISO 21434、TARA、安全评估。 Safety and compliance: functional safety, SOTIF, China compliance, ISO 21434, TARA, safety assessment. functional-safety / sotif / china-compliance / cybersecurity
  • 自动驾驶与 ADAS:感知、规划、控制、自动驾驶系统架构、ODD 与场景工程。 Automated driving and ADAS: perception, planning, control, autonomous-system architecture, ODD, and scenario engineering. adas / testing / validation / vehicle-systems
  • 整车电子与平台:AUTOSAR、HPC、SDV、区域架构、QNX、云端与车云协同。 E/E and platform: AUTOSAR, HPC, SDV, zonal architecture, QNX, cloud, and vehicle-cloud integration. autosar / hpc-platform / sdv-platform / zonal-architecture
  • 车辆子系统:电池、热管理、动力底盘、座舱、诊断、标定、V2X 与硬件安全。 Vehicle subsystems: battery, thermal management, powertrain-chassis, cockpit, diagnostics, calibration, V2X, and hardware safety. battery / powertrain-chassis / cockpit / diagnostics / v2x
  • 过程与协同:项目经理、产品负责人、ASPICE 过程、Tier1/Tier2/Tier3、质量门和多专家编排。 Process and collaboration: project managers, product owners, ASPICE process, Tier1/Tier2/Tier3, quality gates, and multi-expert orchestration. project-management / process-quality / orchestration / oem
Skills

技能方法族 Skill method families

  • 中国标准与安全:GB/T 34590、GB/T 43267、L2/L3/泊车强标、ODD、多支柱和 AI 安全。 China standards and safety: GB/T 34590, GB/T 43267, L2/L3/parking mandatory standards, ODD, multi-pillar, and AI safety. china-standards / automotive-china-*
  • SOTIF 与场景验证:危险场景构建、SOTIF 审核、高速测试、场景驱动测试评价。 SOTIF and scenario validation: hazard scenario construction, SOTIF audit, highway testing, and scenario-driven evaluation. automotive-sotif-* / automotive-scenario-driven-testing
  • 端到端 AD 安全:E2E 安全分析、驾驶员基础模型 DFM、AI ECU、车端 ML 和数据闭环。 End-to-end AD safety: E2E safety analysis, Driver Foundation Model benchmarking, AI ECU, vehicle-side ML, and data loops. automotive-e2e-safety-analysis / automotive-dfm-benchmarking / automotive-ml
  • 软件定义汽车:AUTOSAR、SDV、HPC、区域架构、中间件、OTA、数字孪生和车云集成。 Software-defined vehicle: AUTOSAR, SDV, HPC, zonal architecture, middleware, OTA, digital twins, and cloud integration. autosar / automotive-sdv / automotive-zonal / middleware
  • 验证与工程执行:HIL/SIL/VIL、诊断、标定、网络、充电基础设施、功能安全指标与安全案例。 Verification and execution: HIL/SIL/VIL, diagnostics, calibration, networks, charging infrastructure, functional-safety metrics, and safety cases. hil-sil / diagnostics / calibration / hardware-safety / safety-analysis
Commands / Workflows

可执行任务入口 Executable task entry points

  • ADAS:传感器标定、ODD 定义、场景生成、感知评估。ADAS: sensor calibration, ODD definition, scenario generation, perception evaluation.
  • 安全:HARA、FMEA、FTA、ASIL 分解、安全报告。Safety: HARA, FMEA, FTA, ASIL decomposition, safety reports.
  • 工程:AUTOSAR 生成、诊断刷写、标定、MBD、CI、发布与回滚。Engineering: AUTOSAR generation, diagnostics flashing, calibration, MBD, CI, release and rollback.
  • 流程:ECU 开发、ADAS 开发、安全合规、测试、认证、生产与现场支持。Flows: ECU development, ADAS development, safety compliance, testing, certification, production, and field support.
Rules / Knowledge / Hooks

边界与证据支撑 Boundaries and evidence support

  • 规则库:编码标准、过程标准、测试标准、安全标准、网络安全和中国标准。Rules: coding standards, process standards, testing standards, safety standards, cybersecurity, and China standards.
  • 知识库:ISO 26262、SOTIF、ASPICE 4.0、MISRA、AUTOSAR、UN R155、场景与工具。Knowledge base: ISO 26262, SOTIF, ASPICE 4.0, MISRA, AUTOSAR, UN R155, scenarios, and tools.
  • 质量门:pre-commit、pre-push、pre-merge、post-deploy 等工程检查入口。Quality gates: pre-commit, pre-push, pre-merge, post-deploy, and related engineering checks.

功能安全与 SysML Functional safety and SysML

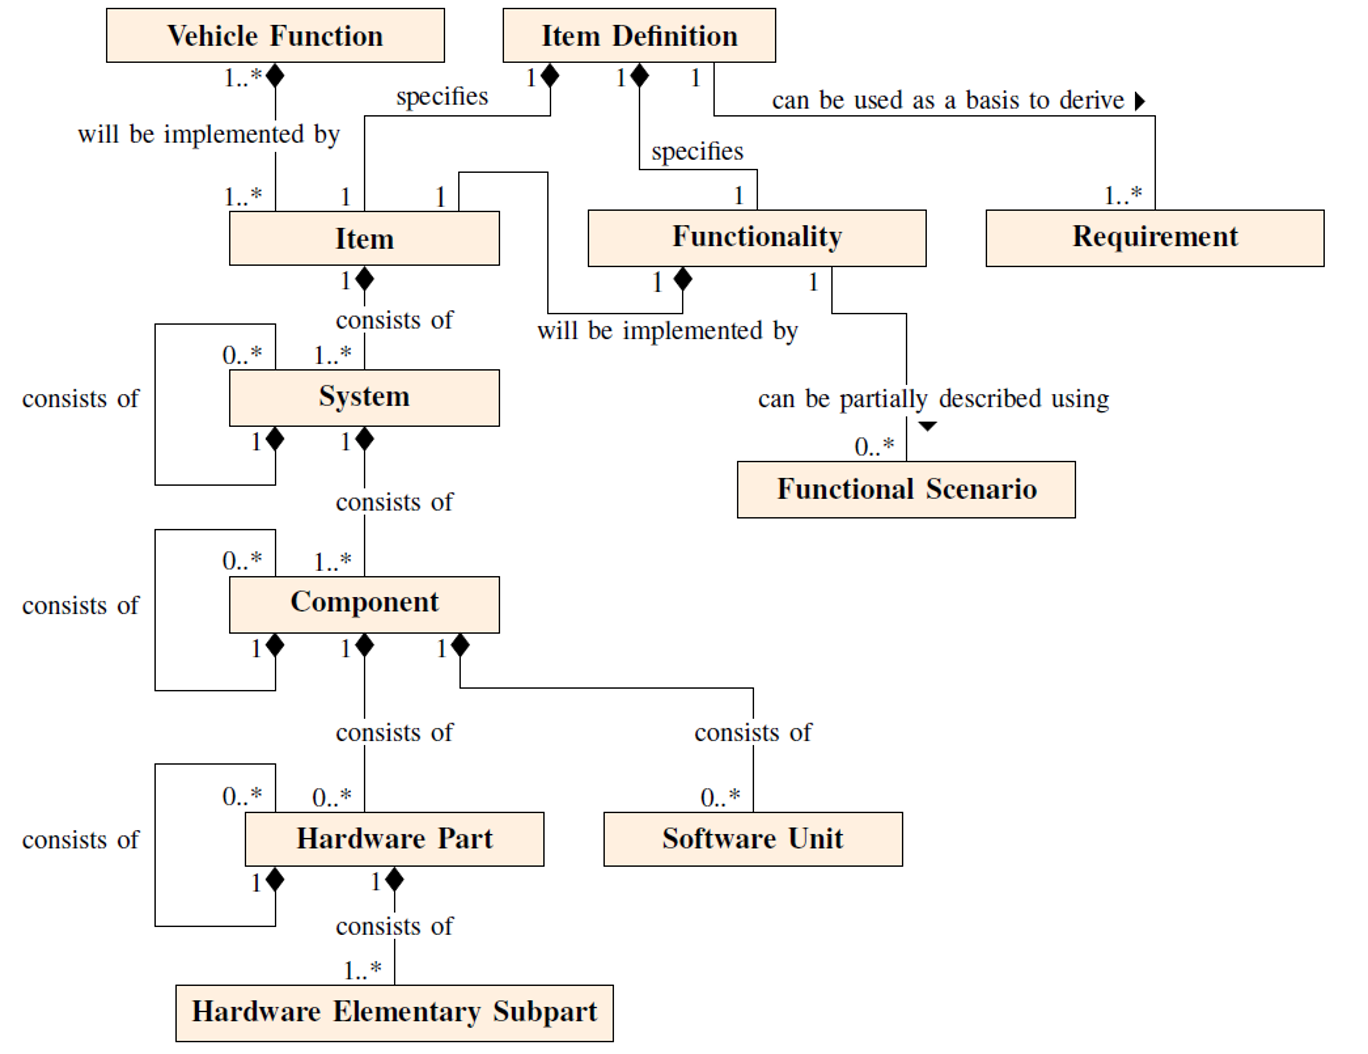
功能安全分析不是孤立写安全目标。它需要把车辆功能、Item Definition、Item、System、Component、硬件部件、软件单元和需求之间的关系结构化表达,才能让架构、规则校核和证据链真正连起来。 Functional-safety analysis is not just writing safety goals. It needs structured relationships among vehicle functions, item definitions, items, systems, components, hardware parts, software units, and requirements so architecture, rule checks, and evidence chains can connect.

Functional safety and SysML object relationship model from vehicle function and item definition to item, system, component, hardware part, software unit and requirement

从文档到模型,再到可复核的智能体工作流 From documents to models, then to reviewable agent workflows

当这些对象关系被模型化,智能体就可以按结构理解需求、架构、安全分析和证据记录,而不是只在长文档里做关键词匹配。 Once these object relationships are modeled, agents can understand requirements, architecture, safety analysis, and evidence records structurally instead of only matching keywords inside long documents.

  • 功能安全对象:Vehicle Function、Item Definition、Item 与 Requirement 形成分析入口。 Safety objects: Vehicle Function, Item Definition, Item, and Requirement form the analysis entry points.
  • 系统建模对象:System、Component、Hardware Part、Software Unit 承接架构分解。 Modeling objects: System, Component, Hardware Part, and Software Unit carry architecture decomposition.
  • 智能体价值:按模型关系检索、生成、校核和沉淀证据,而不是只处理散文档。 Agent value: retrieve, draft, check, and capture evidence by model relationships rather than loose documents.
Item Definition System Component Hardware Part Software Unit Requirement

智能体工作流 Agent workflow

这些资产的价值不只是“有很多文件”,而是可以把概念阶段到系统阶段的工程任务拆成可路由、可复核、可沉淀的步骤。 The value is not simply having many files. The assets help split concept-stage and system-stage engineering tasks into routable, reviewable, and reusable steps.

Agent workflow diagram 输入Input 路由Route 依据Basis 草案Draft 复核Review 沉淀Asset
01

输入问题 Input problem

需求、场景、代码、接口、标准条款、测试问题或架构备选。 Requirements, scenarios, code, interfaces, standards clauses, test issues, or architecture options.

02

角色路由 Role routing

选择安全、SOTIF、场景、架构、测试、中国标准或过程质量视角。 Route through safety, SOTIF, scenario, architecture, testing, China-standard, or process-quality perspectives.

03

检索依据 Retrieve basis

调用技能、规则、知识库、命令模板和示例工作产品。 Use skills, rules, knowledge references, command templates, and example work products.

04

生成草案 Draft output

形成需求澄清、架构分析、安全分析、测试计划或证据清单草稿。 Draft requirement clarifications, architecture analysis, safety analysis, test plans, or evidence lists.

05

工程复核 Engineering review

由工程师判断采纳、修改、驳回、补充证据或升级专家评审。 Engineers decide what to accept, modify, reject, supplement with evidence, or escalate to expert review.

06

沉淀资产 Capture asset

把确认后的结果沉淀到仓库、文档、评审记录或后续工具链。 Capture reviewed outputs in repositories, documents, review records, or downstream toolchains.

技术增强 Technical extensions

AutoZYX-Labs Fork 的重点,是把原有汽车工程 agents 进一步扩展到自动驾驶安全、系统工程和中国场景下更难替代的专业任务。 The AutoZYX-Labs fork extends the original automotive agents toward the harder professional tasks in automated-driving safety, systems engineering, and China-specific engineering contexts.

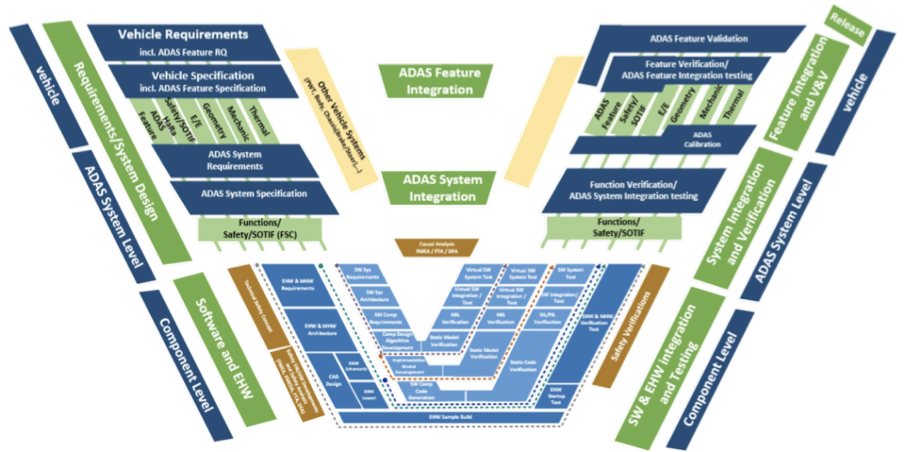
ADAS vehicle requirements, system design, integration, verification and validation V-model

车辆平台Vehicle platform

动力、底盘、EE 架构、域控、传感器和执行器边界。Powertrain, chassis, E/E architecture, domain control, sensors, and actuator boundaries.

自动驾驶系统Automated-driving system

感知、预测、规划、控制、ODD、HMI 和降级策略。Perception, prediction, planning, control, ODD, HMI, and fallback strategy.

安全分析Safety analysis

HARA、FMEA、FTA、STPA、SOTIF 场景和安全论证线索。HARA, FMEA, FTA, STPA, SOTIF scenarios, and safety-argument traces.

测试评价Validation

仿真、场地、道路、多支柱评价、风险场景和证据记录。Simulation, proving ground, road tests, multi-pillar evaluation, risk scenarios, and evidence records.

中国标准与合规 China standards and compliance

覆盖 GB/T 34590、GB/T 43267、CSAE SOTIF、L2/L3/泊车、ODD、多支柱评价和准入材料准备等方向。 Covers GB/T 34590, GB/T 43267, CSAE SOTIF, L2/L3/parking, ODD, multi-pillar evaluation, and approval-material preparation.

GB/T 34590GB/T 43267ODD

SOTIF 深度实践 Deep SOTIF practice

沉淀触发条件识别、危险场景构建、高速公路测试评价、审核评估和成熟度模型等任务入口。 Captures triggering-condition identification, hazardous scenario construction, highway test evaluation, audit review, and maturity-model entry points.

SOTIFTriggering conditionsHazardous scenarios

端到端 AD Safety End-to-end AD safety

面向端到端感知/决策系统,组织安全分析、模型行为边界、驾驶员基础模型基准评测和类人驾驶评价。 Organizes safety analysis, model-behavior boundaries, Driver Foundation Model benchmarking, and human-like driving evaluation for end-to-end AD systems.

E2E ADDFMHuman-like driving

ASPICE 与工程过程 ASPICE and engineering process

以 SYS、SWE、HWE、MLE、VAL、SUP、MAN 等过程域组织角色、模板、检查项和工作产品线索。 Uses SYS, SWE, HWE, MLE, VAL, SUP, and MAN process areas to organize roles, templates, checklists, and work-product traces.

SYSSWEVALSUP

场景驱动测试 Scenario-driven testing

连接 ODD、场景分类、仿真/场地/道路联合验证、风险场景和验证证据链。 Connects ODD, scenario taxonomy, simulation-field-road validation, risk scenarios, and validation evidence chains.

Scenario taxonomySimulationRoad test

系统架构创成(内部版) System architecture generation (internal)

通过 SysArchPilot 把需求输入、知识资产、候选生成、规则评价和证据报告接入可复核的架构创成工作流。 Uses SysArchPilot to connect requirements, knowledge assets, candidate generation, rule evaluation, and evidence reports into a reviewable architecture-generation workflow.

SysArchPilotArchitecture generationEvidence report
automotive-claude-code-agents/
  skills/             技能库:ADAS、SOTIF、安全、中国标准、E2E AD
  agents/             智能体:安全、场景、合规、架构、测试角色
  rules/              规则库:安全、编码、过程、测试、中国标准
  commands/           工程命令:把重复任务收敛为可调用入口
  workflows/          工作流:需求、架构、安全、验证、证据链
  hooks/              质量门:安全检查、提交检查、交付前检查
  knowledge-base/     知识库:标准、过程、技术和工具参考
  examples/           示例:汽车软件、平台、测试与部署样例

公开仓库,而不是口头概念 Public repository, not only a concept

页面展示的是一个可以被打开、审阅和追溯的公开仓库。README、技能目录、智能体定义、规则库、知识库、示例和安装脚本共同证明:这不是一次性演示,而是一组正在沉淀的工程智能体资产。 This page points to a public repository that can be opened, reviewed, and traced. README files, skill directories, agent definitions, rules, knowledge references, examples, and installation scripts together show that this is not a one-off demo, but an evolving engineering-agent asset base.

公开文章和 LinkedIn 传播反馈可作为辅助背景;本页不把传播效果包装成客户验证或商业落地。 Public articles and LinkedIn reception may provide background context; this page does not present public attention as customer validation or commercial adoption.

边界声明 Boundaries

高质量证据页必须守住边界。这个项目可以证明已有公开探索和方法储备,但不能被包装成认证工具、量产平台或客户交付成果。 A credible evidence page must state its boundaries. This project can show public exploration and method preparation, but it should not be presented as a certification tool, production platform, or delivered customer system.

可以这样说 Safe claims

  • 开源探索和前期工作证据 Open exploration and prior-work evidence
  • 汽车研发智能体资产和方法储备 Automotive engineering-agent assets and method base
  • 辅助整理安全工程任务和证据链 Assists safety-engineering tasks and evidence workflows
  • 需要工程师人工复核 Requires engineering review

不能这样说 Do not claim

  • 自动完成安全分析或合规认证 Automatically completes safety analysis or compliance certification
  • 替代功能安全、SOTIF 或标准法规工程师 Replaces functional-safety, SOTIF, or standards engineers
  • 已被客户正式采用或量产验证 Has been formally adopted by customers or production-validated
  • 完全原创且不依赖上游开源项目 Is fully original without upstream open-source roots